Drawing on over 440,000 incidents across the industry, new report helps MSPs identify key security risks and optimize prevention.
ConnectWise Cyber Research Unit (CRU) analyzed over 440,000 incidents that impacted MSPs and their clients and identified the top five ransomware variants used to target MSPs in 2022, some of the biggest vulnerabilities impacting MSPs, and used this data to make predictions about upcoming trends MSP should be aware of.
“The findings of this year’s Threat Report highlight the growing importance of cybersecurity for MSPs and their customers. As the threat landscape continues to evolve, MSPs must remain vigilant and take proactive steps to protect their networks and clients,” commented Patrick Beggs, chief information security officer, ConnectWise. “By adopting a zero-trust network architecture, leveraging threat intelligence research and investing in specialized cybersecurity training, MSPs can stay ahead of the curve and build more effective protection for their mission-critical infrastructure and services. ConnectWise is proud to have a foundation of transparency and an integrated cyber infrastructure that supports reports like this. We can develop and deliver cybersecurity products and services while leveraging the latest threat intelligence to protect our partners – letting them connect with confidence.”
The report includes visuals so MSPs can cross-reference common techniques used and determine which are most likely to impact their business and customers. A heat map of the MITRE ATT&CK techniques and sub-techniques observed during 2022 allows MSPs to be more confident in investing in cybersecurity efforts that will have the most impact in defending against attacks.
One of the significant findings in the report is the emergence of a new phishing technique used by bad actors targeting MSPs. It works by exploiting changes in the default behavior of Visual Basic Application (VBA) macros handled in Microsoft Office documents downloaded online. In 2022, this approach led to a rise in the use of LNK files to deliver payloads, which would then lead to ransomware deployments.
Based on this detailed insight, the report also offers a series of cybersecurity predictions for MSP in 2023 and beyond:
Forging the Next 250 Years: Powering the Next Era of American Manufacturing
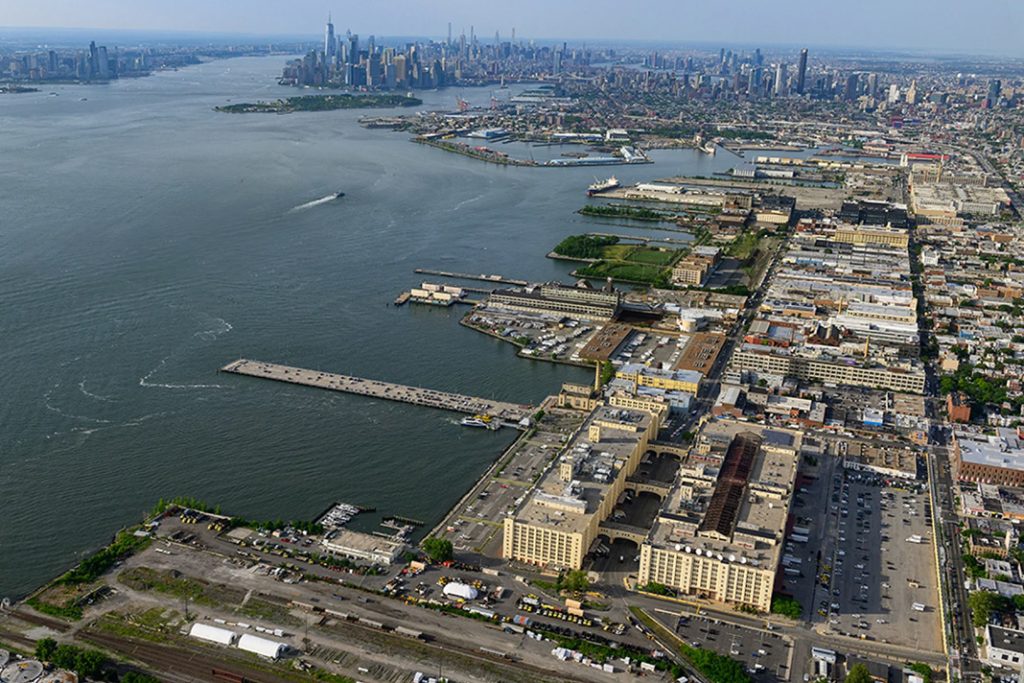
Brooklyn Army Terminal (BAT) began as a World War II-era military supply base. Today it is New York City’s largest publicly owned industrial campus, with 59 waterfront acres, more than 4 million square feet and over 100 businesses. In this episode of Industry Insights, Bridget Chansakul, Vice President of Leasing & Portfolio Management at NYCEDC, explains what space is available and what’s planned for the 250,000+ square feet of new industrial space in Building A. She also covers how the ferry, parking and on-site childcare help tenants hire and keep workers, along with workforce partnerships, City incentives for manufacturers and where BAT is headed next.
Get In Touch
Google news and SEO compliant, Industry Today’s state-of-the-art digital media platform offers bespoke media campaigns that target key decision makers and buyers to achieve your marketing and promotional goals.
Contribute
Showcase your brand and promote your business to our highly targeted audience. We offer detailed Google Analytics with measurable ROI to assure success. Submit your content for review by our Editorial team who will contact you to discuss the project further.
About Us
Reach Your Targeted Audience and Grow Your Business. Learn more About Industry Today.
Contact Us
© 2026 Industry today. All Rights reserved.